Packs reference
A pack is a maintained set of standards for one topic. Groundrule bundles 13 packs with 171 standards: 93 with a deterministic check and 78 that are guidance for agents and reviewers. This page lists every pack and every standard in it. The packs are open source, in packages/packs/catalog.
Use a pack
Section titled “Use a pack”With a connected workspace, you choose packs in the dashboard, under Packs, and each repository gets them through groundrule sync. Onboarding preselects the packs that fit your stack. See Adopting rules.
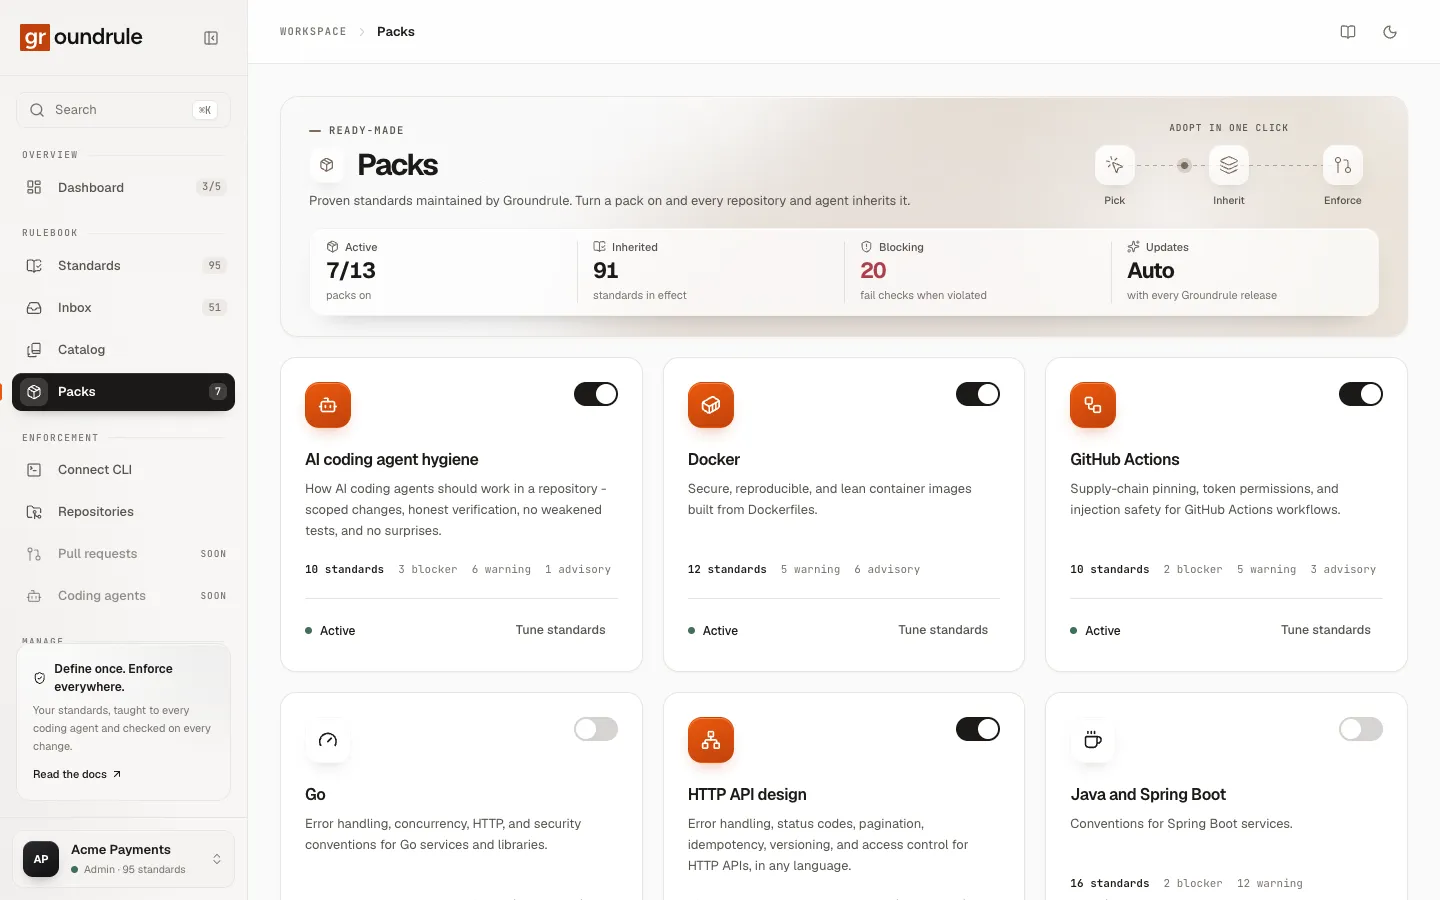
Offline, add packs to extends in .groundrule/config.yaml:
extends: - groundrule:packs/security-baseline - groundrule:packs/typescript-nodeOr choose them when you create the config:
npx @groundrule/cli init --packs security-baseline,typescript-nodeWithout --packs, init picks security-baseline, plus typescript-node when it finds TypeScript or JavaScript, and java-spring when it finds Java.
npx @groundrule/cli packs lists the bundled packs with their standards counts. Packs ship inside the CLI, so a newer CLI version brings pack updates. A version in the reference, such as groundrule:packs/react@1.0.0, is accepted but not used yet: you always get the version bundled with your CLI.
To change a pack rule in one repository, see Overrides and exceptions. To build your own pack, see Packs of your own below.
Reading the tables
Section titled “Reading the tables”| Column | Meaning |
|---|---|
| Severity | blocker, warning, advisory or info. |
| How it’s checked | Check and the evaluators it uses, or Guidance when the rule has no check and only reaches agents and reviewers. See Checks. |
| Starts at | The recommended stage when you adopt it (rollout.recommendedStage). Your workspace starts the rule there. See Rollout stages. |
| Noise | How often the check flags code that is fine: Low (almost always real), Medium (occasional false positives), High (expect to tune scope). |
Some packs are relevant only to some repositories, for example the Docker pack to repositories with a Dockerfile. That is used for recommendations only. Rules that need a language or framework, such as the React rules, are left out of repositories without it, and groundrule standards shows them as (not applicable here). npx @groundrule/cli explain <ID> shows any rule in full: requirement, why, examples, fix, references, compliance mappings and known false positives.
AI coding agent hygiene
Section titled “AI coding agent hygiene”groundrule:packs/agent-hygiene · version 1.0.0 · 10 standards
How AI coding agents should work in a repository: scoped changes, honest verification, no weakened tests, and no surprises.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
AGENT-001 |
Regenerate generated files; never edit them by hand | warning | Guidance | Teach | Low |
AGENT-002 |
Justify every new dependency and prefer what the project already uses | warning | Guidance | Teach | Low |
AGENT-003 |
Keep changes scoped to the task | warning | Guidance | Teach | Low |
AGENT-004 |
Run the project’s checks before declaring the work done | warning | Guidance | Teach | Low |
AGENT-005 |
Never weaken tests or checks to get a green build | blocker | Guidance | Teach | Low |
AGENT-006 |
Ask before destructive or irreversible operations | blocker | Guidance | Teach | Low |
AGENT-007 |
Follow existing patterns before introducing new ones | warning | Guidance | Teach | Low |
AGENT-008 |
Update docs, examples, and the changelog when behavior changes | advisory | Guidance | Teach | Low |
AGENT-009 |
State assumptions, open questions, and unverified parts | warning | Guidance | Teach | Low |
AGENT-010 |
No merge conflict markers or merge leftovers | blocker | Check: regex, files | Enforce | Low |
Docker
Section titled “Docker”groundrule:packs/docker · version 1.0.0 · 12 standards
Secure, reproducible, and lean container images built from Dockerfiles.
Relevant to repositories with any of: files **/Dockerfile, **/Dockerfile.*, **/*.dockerfile.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
DOCKER-001 |
Run the final image as a non-root user | warning | Check: regex | Advise | Medium |
DOCKER-002 |
Pin base images to a version tag or digest | warning | Check: regex | Enforce | Low |
DOCKER-003 |
Use COPY for local files, not ADD | advisory | Check: regex | Advise | Medium |
DOCKER-004 |
Do not pipe downloaded scripts into a shell | warning | Check: regex | Advise | Low |
DOCKER-005 |
Do not pass secrets through ENV or ARG | warning | Check: regex | Advise | Medium |
DOCKER-006 |
Run apt-get update and install in the same RUN | warning | Check: regex | Enforce | Low |
DOCKER-007 |
Install apt packages with –no-install-recommends | advisory | Check: regex | Advise | Medium |
DOCKER-008 |
Use the exec form for CMD and ENTRYPOINT | advisory | Check: regex | Advise | Medium |
DOCKER-009 |
Keep a .dockerignore next to every build context | advisory | Guidance | Teach | Low |
DOCKER-010 |
Use multi-stage builds to keep toolchains out of runtime images | advisory | Guidance | Teach | Low |
DOCKER-011 |
Order Dockerfile steps for layer caching | info | Guidance | Teach | Low |
DOCKER-012 |
Get OS patches by updating the base image | advisory | Guidance | Teach | Low |
GitHub Actions
Section titled “GitHub Actions”groundrule:packs/github-actions · version 1.0.0 · 10 standards
Supply-chain pinning, token permissions, and injection safety for GitHub Actions workflows.
Relevant to repositories with any of: files .github/workflows/*.yml, .github/workflows/*.yaml.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
GHA-001 |
Pin third-party actions to a full commit SHA | warning | Check: regex | Advise | Low |
GHA-002 |
Declare minimal token permissions in every workflow | warning | Check: regex | Advise | Medium |
GHA-003 |
Do not interpolate untrusted event data into scripts | blocker | Check: regex | Enforce | Low |
GHA-004 |
Do not check out pull request code in pull_request_target workflows | blocker | Check: regex | Advise | Medium |
GHA-005 |
Do not pipe downloaded scripts into a shell in workflows | warning | Check: regex | Advise | Medium |
GHA-006 |
Authenticate to cloud providers with OIDC, not long-lived keys | warning | Check: regex | Advise | Medium |
GHA-007 |
Pass secrets to steps through env and never print them | warning | Guidance | Teach | Low |
GHA-008 |
Do not persist checkout credentials unless a later step pushes | advisory | Guidance | Teach | Low |
GHA-009 |
Bound job runtime and cancel superseded runs | advisory | Guidance | Teach | Low |
GHA-010 |
Deploy through protected environments | advisory | Guidance | Teach | Low |
groundrule:packs/go · version 1.0.0 · 13 standards
Error handling, concurrency, HTTP, and security conventions for Go services and libraries.
Relevant to repositories with any of: languages go; files **/go.mod.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
GO-001 |
Handle every returned error | warning | Guidance | Teach | Low |
GO-002 |
Wrap errors with %w, not %v | advisory | Check: regex | Advise | Medium |
GO-003 |
Do not panic in library code | advisory | Check: regex | Advise | Medium |
GO-004 |
Pass context.Context as the first parameter | warning | Guidance | Teach | Low |
GO-005 |
Give every goroutine a way to stop | warning | Guidance | Teach | Low |
GO-006 |
Do not make HTTP calls without a timeout | warning | Check: regex | Advise | Medium |
GO-007 |
Set timeouts on HTTP servers | warning | Check: regex | Advise | Low |
GO-008 |
Use query placeholders, not fmt.Sprintf, to build SQL | blocker | Check: regex | Advise | Medium |
GO-009 |
Use crypto/rand for security-sensitive random values | warning | Check: regex | Advise | Low |
GO-010 |
No fmt.Print in library code | advisory | Check: regex | Advise | Medium |
GO-011 |
No unmaintained JWT and UUID modules | warning | Check: dependencies | Enforce | Low |
GO-012 |
Close resources with defer right after acquiring them | warning | Guidance | Teach | Low |
GO-013 |
Run gofmt, go vet, and tests with the race detector in CI | advisory | Guidance | Teach | Low |
HTTP API design
Section titled “HTTP API design”groundrule:packs/http-api · version 1.0.0 · 12 standards
Error handling, status codes, pagination, idempotency, versioning, and access control for HTTP APIs, in any language.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
HTTP-001 |
Return one documented error shape and never expose internals | warning | Check: regex | Advise | Low |
HTTP-002 |
Use the status code that matches the outcome | warning | Guidance | Teach | Low |
HTTP-003 |
Paginate every list endpoint with a server-enforced maximum page size | warning | Guidance | Teach | Low |
HTTP-004 |
Make side-effecting POST requests safe to retry with idempotency keys | warning | Guidance | Teach | Low |
HTTP-005 |
Do not make breaking changes to a published API version | blocker | Guidance | Teach | Low |
HTTP-006 |
Validate every request against a schema and never bind it straight to a model | warning | Guidance | Teach | Low |
HTTP-007 |
Authenticate and authorize every endpoint, denying by default | blocker | Guidance | Teach | Low |
HTTP-008 |
Rate limit authentication and expensive endpoints | warning | Guidance | Teach | Low |
HTTP-009 |
Use unambiguous formats for timestamps and money | advisory | Guidance | Teach | Low |
HTTP-010 |
Expose opaque public identifiers, not database keys | advisory | Guidance | Teach | Low |
HTTP-011 |
Update the API description in the same change as the API | warning | Guidance | Teach | Low |
HTTP-012 |
Follow the API’s existing naming and resource conventions | advisory | Guidance | Teach | Low |
Java and Spring Boot
Section titled “Java and Spring Boot”groundrule:packs/java-spring · version 1.1.0 · 16 standards
Conventions for Spring Boot services.
Relevant to repositories with any of: languages java; frameworks spring-boot; files **/pom.xml, **/build.gradle, **/build.gradle.kts.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
JAVA-001 |
Use constructor injection | warning | Check: regex | Advise | Low |
JAVA-002 |
Log with the logging framework | warning | Check: regex | Advise | Low |
JAVA-003 |
Controllers must not use repositories directly | warning | Check: regex | Advise | Medium |
JAVA-004 |
Keep business logic out of controllers | warning | Guidance | Teach | Low |
JAVA-005 |
Put @Transactional on services, not controllers | warning | Check: regex | Advise | Low |
JAVA-006 |
Do not put @Transactional on private methods | warning | Check: regex | Enforce | Low |
JAVA-007 |
Do not build SQL or JPQL by string concatenation | blocker | Check: regex | Advise | Medium |
JAVA-008 |
No literal secrets in Spring configuration files | blocker | Check: regex | Advise | Medium |
JAVA-009 |
Do not expose all Actuator endpoints over HTTP | warning | Check: regex | Advise | Low |
JAVA-010 |
Justify every CSRF disable in Spring Security | warning | Check: regex | Advise | Medium |
JAVA-011 |
Use SLF4J placeholders, not string concatenation, in log calls | advisory | Check: regex | Advise | Low |
JAVA-012 |
Use java.time instead of Date, Calendar, and SimpleDateFormat | advisory | Check: regex | Advise | Low |
JAVA-013 |
Do not use Lombok @Data on JPA entities | warning | Check: regex | Advise | Low |
JAVA-014 |
Never bind request bodies to JPA entities | warning | Guidance | Teach | Low |
JAVA-015 |
Validate request DTOs with Bean Validation and @Valid | warning | Guidance | Teach | Low |
JAVA-016 |
Handle exceptions centrally; never swallow them | warning | Guidance | Teach | Low |
Kubernetes
Section titled “Kubernetes”groundrule:packs/kubernetes · version 1.0.0 · 12 standards
Secure and reliable Kubernetes manifests, aligned with the Pod Security Standards.
Relevant to repositories with any of: files **/k8s/**, **/kubernetes/**, **/manifests/**, **/charts/**, **/kustomization.yaml, **/kustomization.yml.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
K8S-001 |
No privileged containers | blocker | Check: regex | Enforce | Low |
K8S-002 |
Do not share the host network, PID, or IPC namespace | blocker | Check: regex | Advise | Low |
K8S-003 |
Set allowPrivilegeEscalation to false | warning | Check: regex | Advise | Medium |
K8S-004 |
Require runAsNonRoot | warning | Check: regex | Advise | Medium |
K8S-005 |
Harden pod security contexts to the restricted profile | warning | Guidance | Teach | Low |
K8S-006 |
Set resource requests for every container | warning | Check: regex | Advise | Medium |
K8S-007 |
Pin container images to a version tag or digest | warning | Check: regex | Advise | Medium |
K8S-008 |
Do not commit Secret manifests with values | blocker | Check: regex | Advise | Low |
K8S-009 |
Give long-running containers readiness and liveness probes | warning | Guidance | Teach | Low |
K8S-010 |
Restrict pod traffic with NetworkPolicies | advisory | Guidance | Teach | Low |
K8S-011 |
Deploy workloads to a dedicated namespace, not default | advisory | Guidance | Teach | Low |
K8S-012 |
No wildcard RBAC rules or cluster-admin bindings | warning | Check: regex | Advise | Low |
Python
Section titled “Python”groundrule:packs/python · version 1.0.0 · 16 standards
Low-noise correctness, security, and maintainability conventions for Python codebases.
Relevant to repositories with any of: languages python; files **/pyproject.toml, **/requirements*.txt, **/setup.py.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
PY-001 |
No bare except clauses | warning | Check: regex | Enforce | Low |
PY-002 |
No mutable default arguments | warning | Check: regex | Enforce | Low |
PY-003 |
No print() in application code | warning | Check: regex | Advise | Medium |
PY-004 |
Do not unpickle data you did not produce | warning | Check: regex | Advise | Medium |
PY-005 |
Load YAML with yaml.safe_load | blocker | Check: regex | Enforce | Low |
PY-006 |
Run subprocesses without a shell | warning | Check: regex | Advise | Medium |
PY-007 |
No eval or exec | blocker | Check: regex | Enforce | Low |
PY-008 |
No wildcard imports | advisory | Check: regex | Enforce | Low |
PY-009 |
Set a timeout on every requests call | warning | Check: regex | Advise | Medium |
PY-010 |
Use timezone-aware datetimes instead of utcnow() | warning | Check: regex | Enforce | Low |
PY-011 |
Never enable Django or Flask debug mode in deployable code | blocker | Check: regex | Advise | Medium |
PY-012 |
Do not use assert for runtime validation | warning | Guidance | Teach | Low |
PY-013 |
Type-annotate public functions | advisory | Guidance | Teach | Low |
PY-014 |
Declare project metadata and tool settings in pyproject.toml | advisory | Guidance | Teach | Low |
PY-015 |
Use module loggers with lazy formatting | advisory | Guidance | Teach | Low |
PY-016 |
Use the secrets module for security-sensitive randomness | warning | Guidance | Teach | Low |
groundrule:packs/react · version 1.0.0 · 12 standards
Security, accessibility, and correctness conventions for React applications.
Relevant to repositories with any of: frameworks react; files **/package.json.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
REACT-001 |
Sanitize HTML passed to dangerouslySetInnerHTML | warning | Check: regex | Advise | Medium |
REACT-002 |
Use stable IDs, not array indexes, as list keys | advisory | Check: regex | Advise | Medium |
REACT-003 |
Add rel=“noopener noreferrer” to target=“_blank” links | advisory | Check: regex | Advise | Low |
REACT-004 |
Use refs, not document queries, inside components | advisory | Check: regex | Advise | Medium |
REACT-005 |
Follow the Rules of Hooks | warning | Guidance | Teach | Low |
REACT-006 |
Give every img an alt attribute | warning | Check: regex | Advise | Low |
REACT-007 |
Use buttons and links for interactive elements | warning | Guidance | Teach | Low |
REACT-008 |
No secrets in client-exposed environment variables | blocker | Check: regex | Enforce | Low |
REACT-009 |
Write function components with hooks | advisory | Guidance | Teach | Low |
REACT-010 |
Fetch data through the project’s data layer | advisory | Guidance | Teach | Low |
REACT-011 |
Do not use effects for derived state or event logic | advisory | Guidance | Teach | Low |
REACT-012 |
Keep rendering pure and state immutable | warning | Guidance | Teach | Low |
Security baseline
Section titled “Security baseline”groundrule:packs/security-baseline · version 1.1.0 · 20 standards
Secrets, credentials, TLS, and supply-chain basics every repository should follow.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
SEC-001 |
No private keys in the repository | blocker | Check: regex | Enforce | Low |
SEC-002 |
No environment files in the repository | blocker | Check: files | Enforce | Low |
SEC-003 |
No access tokens in code | blocker | Check: regex | Enforce | Low |
SEC-004 |
Do not disable TLS verification | blocker | Check: regex | Advise | Medium |
SEC-005 |
Commit a dependency lockfile | warning | Check: files | Enforce | Low |
SEC-006 |
Never log secrets or personal data | warning | Guidance | Teach | Low |
SEC-007 |
No Google API keys in code | warning | Check: regex | Advise | Medium |
SEC-008 |
No Slack webhook URLs in code | blocker | Check: regex | Enforce | Low |
SEC-009 |
No npm access tokens in code or .npmrc | blocker | Check: regex | Enforce | Low |
SEC-010 |
No Azure storage or Service Bus keys in connection strings | blocker | Check: regex | Enforce | Low |
SEC-011 |
No SSH keys or key stores in the repository | blocker | Check: files | Enforce | Low |
SEC-012 |
No hard-coded passwords or secrets in string literals | warning | Check: regex | Advise | Medium |
SEC-013 |
Do not enable SSLv3, TLS 1.0, or TLS 1.1 | warning | Check: regex | Enforce | Low |
SEC-015 |
Use parameterized queries, never string-built SQL | blocker | Guidance | Teach | Low |
SEC-016 |
Never deserialize untrusted data with native object serializers | blocker | Guidance | Teach | Low |
SEC-017 |
Set Secure, HttpOnly, and SameSite on session cookies | warning | Guidance | Teach | Low |
SEC-018 |
Restrict CORS to an allow list of trusted origins | warning | Guidance | Teach | Low |
SEC-019 |
Verify JWT signature, algorithm, and expiry | blocker | Guidance | Teach | Low |
SEC-020 |
Validate destinations before making server-side requests to user-supplied URLs | warning | Guidance | Teach | Low |
SEC-021 |
Generate tokens and secrets with a cryptographically secure random generator | warning | Guidance | Teach | Low |
Terraform
Section titled “Terraform”groundrule:packs/terraform · version 1.0.0 · 12 standards
Credentials, state, supply-chain pinning, and network exposure rules for Terraform code.
Relevant to repositories with any of: languages terraform; files **/*.tf.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
TF-001 |
No hard-coded credentials in Terraform | blocker | Check: regex | Advise | Medium |
TF-002 |
Constrain Terraform and provider versions | warning | Guidance | Teach | Low |
TF-003 |
Commit the Terraform dependency lock file | warning | Check: files | Advise | Medium |
TF-004 |
Pin module sources to a version | warning | Check: regex | Enforce | Low |
TF-005 |
Do not open SSH or RDP to the internet | blocker | Check: regex | Enforce | Low |
TF-006 |
Do not make storage buckets public | blocker | Check: regex | Advise | Medium |
TF-007 |
No Terraform state files in the repository | blocker | Check: files | Enforce | Low |
TF-008 |
Do not commit the .terraform directory | warning | Check: files | Enforce | Low |
TF-009 |
Keep secrets out of tfvars and mark secret variables sensitive | warning | Guidance | Teach | Low |
TF-010 |
Use a remote backend with state locking | warning | Guidance | Teach | Low |
TF-011 |
Enable encryption at rest for data stores | warning | Guidance | Teach | Low |
TF-012 |
Give variables and outputs a type and description | info | Guidance | Teach | Low |
Testing
Section titled “Testing”groundrule:packs/testing · version 1.0.0 · 11 standards
Keep test suites trustworthy, deterministic, and honest, across JavaScript, Python, Java, Go, and Ruby.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
TEST-001 |
Do not commit focused tests | blocker | Check: regex | Enforce | Low |
TEST-002 |
Every skipped test states why | warning | Check: regex | Advise | Low |
TEST-003 |
Unit tests do not call real external services | warning | Guidance | Teach | Low |
TEST-004 |
Fix bugs with a regression test that fails first | warning | Guidance | Teach | Low |
TEST-005 |
Wait for conditions, not fixed sleeps, in tests | warning | Check: regex | Advise | Medium |
TEST-006 |
Control time, randomness, and shared state in tests | warning | Guidance | Teach | Low |
TEST-007 |
Name tests after the behavior they verify | advisory | Guidance | Teach | Low |
TEST-008 |
Review snapshot and golden-file changes; never update them blindly | warning | Guidance | Teach | Low |
TEST-009 |
Test new and changed behavior, not coverage numbers | advisory | Guidance | Teach | Low |
TEST-010 |
Mock at the system boundary and assert on outcomes | advisory | Guidance | Teach | Low |
TEST-011 |
Do not commit test results or coverage output | warning | Check: files | Enforce | Low |
TypeScript and Node.js
Section titled “TypeScript and Node.js”groundrule:packs/typescript-node · version 1.1.0 · 15 standards
Low-noise conventions for TypeScript and JavaScript codebases.
Relevant to repositories with any of: languages typescript, javascript; files **/package.json, **/tsconfig.json.
| ID | Title | Severity | How it’s checked | Starts at | Noise |
|---|---|---|---|---|---|
TS-001 |
No console.log in application code | warning | Check: regex | Advise | Medium |
TS-002 |
No deprecated HTTP and UUID packages | warning | Check: dependencies | Enforce | Low |
TS-003 |
No eval or new Function | blocker | Check: regex | Enforce | Low |
TS-004 |
Prefer @ts-expect-error over @ts-ignore | advisory | Check: regex | Advise | Low |
TS-005 |
Type and validate at the boundaries | warning | Guidance | Teach | Low |
TS-006 |
Await or handle every promise | warning | Guidance | Teach | Low |
TS-007 |
Keep TypeScript strict mode on | warning | Check: regex | Advise | Low |
TS-008 |
Narrow types instead of asserting them | advisory | Guidance | Teach | Low |
TS-009 |
Import Node.js built-ins with the node: prefix | info | Check: regex | Advise | Medium |
TS-010 |
Only entry points call process.exit | warning | Guidance | Teach | Low |
TS-011 |
No deprecated Buffer() constructor | warning | Check: regex | Enforce | Low |
TS-012 |
No blocking synchronous I/O on request paths | warning | Guidance | Teach | Low |
TS-013 |
Type caught errors as unknown, not any | advisory | Check: regex | Advise | Low |
TS-014 |
No debugger statements | warning | Check: regex | Enforce | Low |
TS-015 |
Declare the supported Node.js version in package.json | advisory | Guidance | Teach | Low |
Packs of your own
Section titled “Packs of your own”A pack is a folder with a pack.yaml and a standards/ folder:
apiVersion: groundrule.dev/v1alpha1kind: Packmetadata: id: backend title: Acme backend standards description: Rules every Acme backend service follows. owner: team:platform version: 1.2.0 tags: [backend]spec: include: ["standards/**/*.yaml"] extends: - groundrule:packs/security-baseline| Field | Required | Default | Description |
|---|---|---|---|
metadata.id |
Yes | Lowercase letters, digits and dashes, for example backend. |
|
metadata.title |
Yes | Up to 120 characters. | |
metadata.description |
No | One sentence. | |
metadata.owner |
No | Who maintains it. | |
metadata.version |
No | A semantic version, such as 1.2.0. Bump it whenever a standard changes. |
|
metadata.tags |
No | Discovery tags, such as security. |
|
spec.include |
No | ["standards/**/*.yaml"] |
Standard files, relative to pack.yaml. |
spec.extends |
No | [] |
Other packs this one builds on, with the same references as extends in the config. |
spec.applicability |
No | Which repositories it is relevant to, for recommendations only. |
Repositories extend it with a path or a GitHub reference:
extends: - ../packs/backend # packs/backend in this repository - github:acme-payments/engineering-standards//packs/backend@v1 # pinned to a tagA local path is relative to the file that declares it. In .groundrule/config.yaml, ../packs/backend is the packs/backend folder at the repository root.
A folder without pack.yaml works too: every .yaml file in it is loaded as a standard. GitHub references are fetched with git, so private repositories need git access on the machine. See Environment and files.